When a spreadsheet stops being enough
Most businesses run on a few spreadsheets, a shared inbox and one person who knows how it all fits. The signs that a process has outgrown them, and what a small custom app does differently.
That's the job. We make shipping software boring by designing, building and fixing the platforms your engineers ship on.
These are fixable problems, and none of them needs a big-bang rewrite.
Releases are an event
Shipping needs a checklist, a quiet afternoon and the one person who remembers how it works.
Kubernetes, but nobody's quite sure how
The cluster grew by accident, every namespace is a little different, and nobody wants to do the upgrade.
Infrastructure lives in someone's head
Changes happen in the console, environments drift, and rebuilding one from scratch would take weeks.
The platform team is the bottleneck
Every new service waits on a ticket to the one team that understands the setup.
Kubernetes and internal developer platforms that give your teams a paved road to production.
Learn more
Reproducible infrastructure and CI/CD pipelines that make releasing software a non-event.
Learn more
Move workloads onto AWS, Google Cloud or Azure step by step, without a big-bang cutover.
Learn more
An independent look at your platform, and hands-on training so your team can own it with confidence.
Learn more
Heyal Solutions is led by Alistair Hey, a cloud native platform engineer, and works with a small network of trusted senior associates. You get experienced people without the overhead of a big consultancy.
How engagements work
Most businesses run on a few spreadsheets, a shared inbox and one person who knows how it all fits. The signs that a process has outgrown them, and what a small custom app does differently.

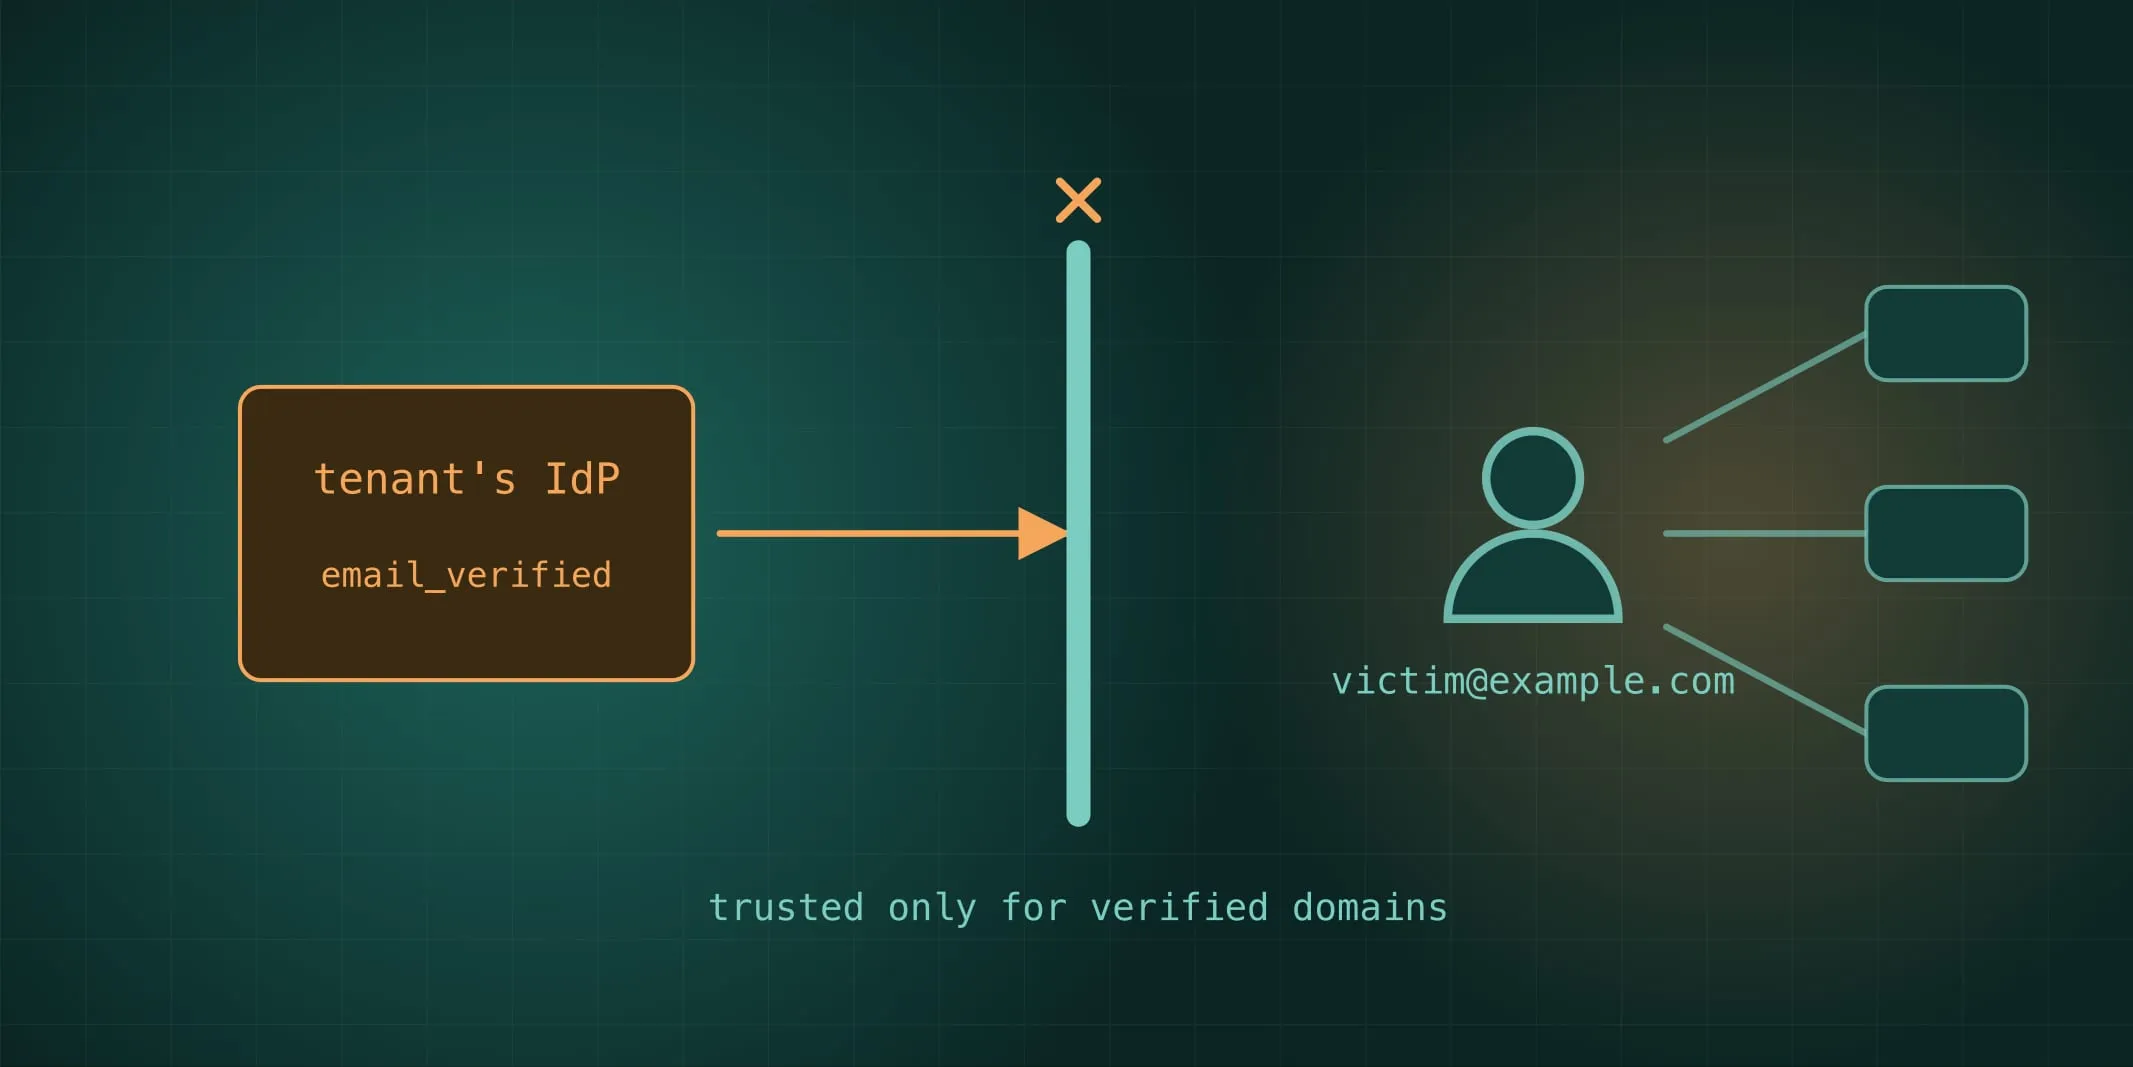
The cross-tenant account takeover hiding in per-tenant SSO: a customer's own identity provider can assert any email it likes. Why an email claim is trusted only for that tenant's verified domains, and linking needs proof.

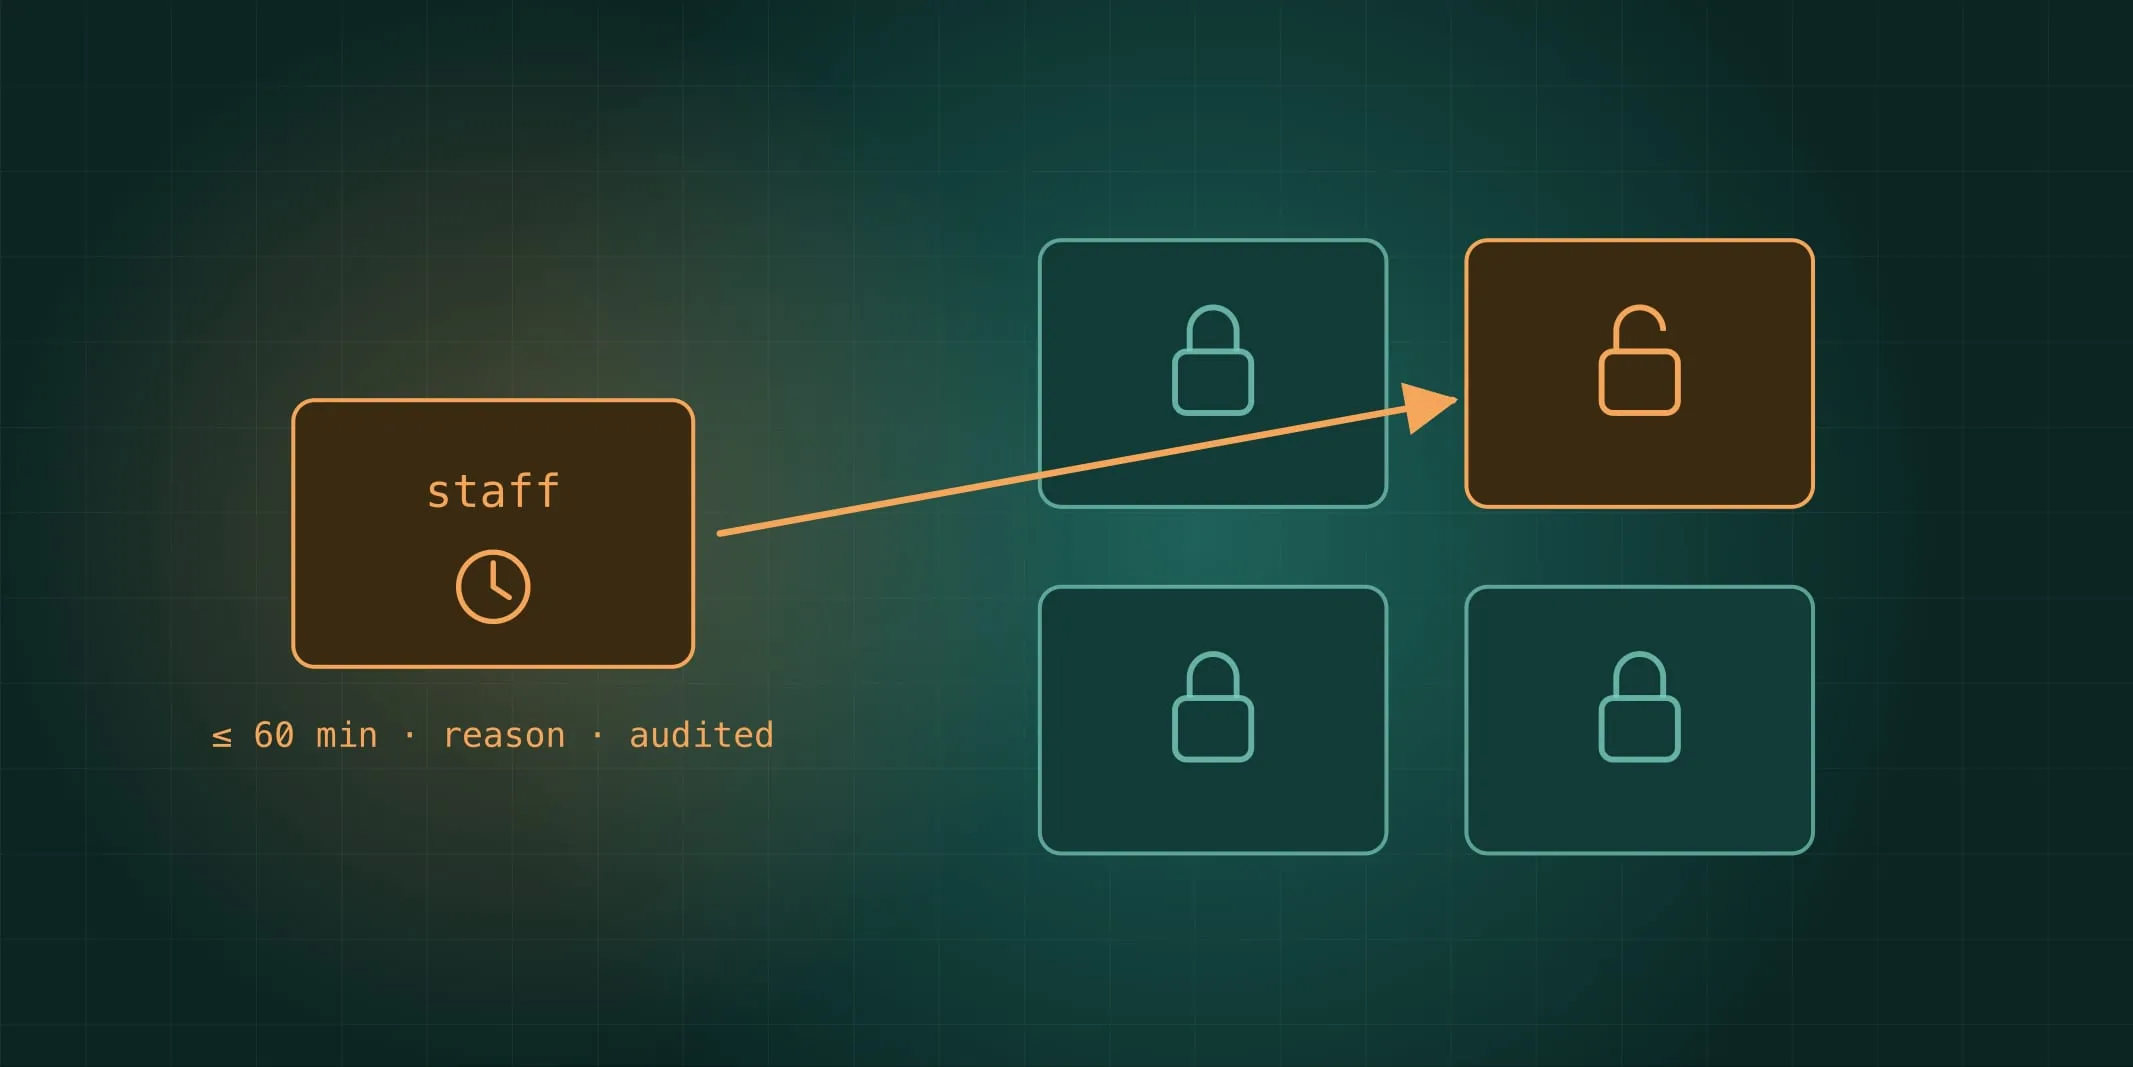
Support staff need to see what customers see. A global bypass role is the wrong way to do it. Time-boxed, audited impersonation grants instead, and what that means for kubectl, logs and database access.
Tell us what you're running and where it hurts. We'll tell you honestly whether we can help.